Among the main challenges facing growing companies, Fource Consultoria, a consultancy specializing in market intelligence, business restructuring, and asset management, recognizes internal controls as one of the most effective tools for reducing operational risks. As operations expand, the number of transactions, suppliers, and people authorized to make decisions increases, and information begins to flow through channels that are less visible to management. Without clear verification procedures, small errors accumulate and only become apparent after they have affected margins, deadlines, or contracts.
What Are Internal Controls in Day-to-Day Business Operations?
Internal controls comprise the set of policies, procedures, and checks that ensure a company operates as planned. They range from two-level payment approvals to periodic inventory and bank account reconciliations. The most widely used framework for organizing this subject is the COSO model, developed in the United States, which divides the system into five components: control environment, risk assessment, control activities, information and communication, and monitoring. Although originally developed for large corporations, the framework can be adapted to businesses of different sizes and across various sectors.
According to Fource Consultoria, the value of this model lies less in its sophistication than in the interconnected logic it proposes. A weak control environment compromises risk assessment, which in turn undermines verification activities. At the same time, well-designed controls lose their effectiveness when the information they produce does not reach the people who need to make decisions. Integration among the components, therefore, matters just as much as the quality of each one individually. Without this integration, companies accumulate checks that do not communicate with one another and generate more bureaucracy than protection.
Where Do Operational Risks Usually Hide?
The most vulnerable points are rarely found in the most closely monitored areas. They often emerge in processes considered routine, such as supplier registration, contract adjustments, system access management, and invoice issuance. When a single person handles tasks that should be separated, such as registering, approving, and paying a supplier, operational risk multiplies, even when there is no malicious intent. Typing errors, duplicate entries, and overdue payments go unnoticed due to the lack of a second review. In many cases, the problem only becomes apparent during the accounting close, when correcting it is already more expensive.
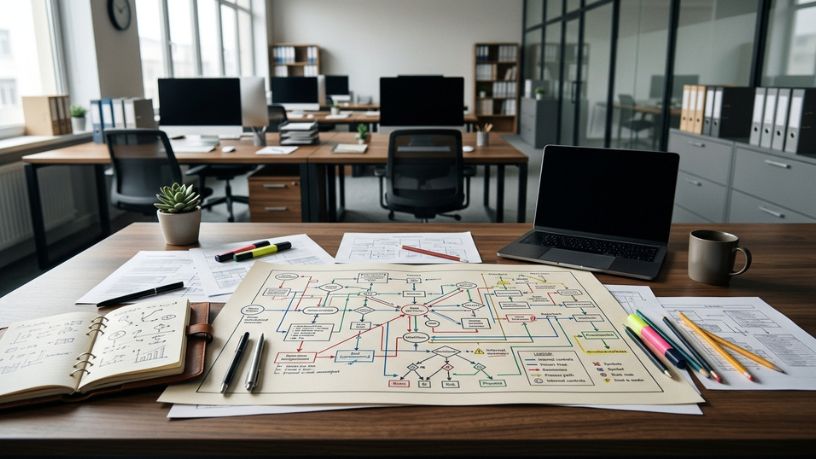
Mapping these points requires tracing the entire flow of each process, from the initial request to the accounting entry, identifying where information changes hands. At these transition points, Fource Consultoria Empresarial assesses the exposure associated with each stage by combining the likelihood of failure with its potential financial and operational impact. The result is a risk matrix that helps prioritize resources, concentrating stronger controls where potential losses are greater and simplifying those that add little value. The matrix also serves as a reference for training teams and reviewing procedures.
Controls Proportionate to Company Size
A common mistake is to import structures from large corporations into mid-sized companies, creating layers of approval that make operations slow and expensive. Excessive controls generate rework, discourage teams, and, paradoxically, encourage informal workarounds. As Fource Consultoria explains, each control must have a cost proportionate to the risk it mitigates and a clearly designated person responsible for its execution. Automated checks in management systems, for example, often offer a better alternative to time-consuming manual reviews. In smaller companies, simplicity is often an ally of effectiveness.
Another relevant aspect is the periodic review of the system itself. Changes in the business model, entry into new markets, or system replacements alter the risk landscape and may render previously appropriate controls obsolete. The so-called Three Lines Model, widely referenced in international governance guidelines, organizes these responsibilities across operational management, risk functions, and independent assessment. Companies that incorporate this review into their management calendar tend to adjust their controls before failures affect business results.