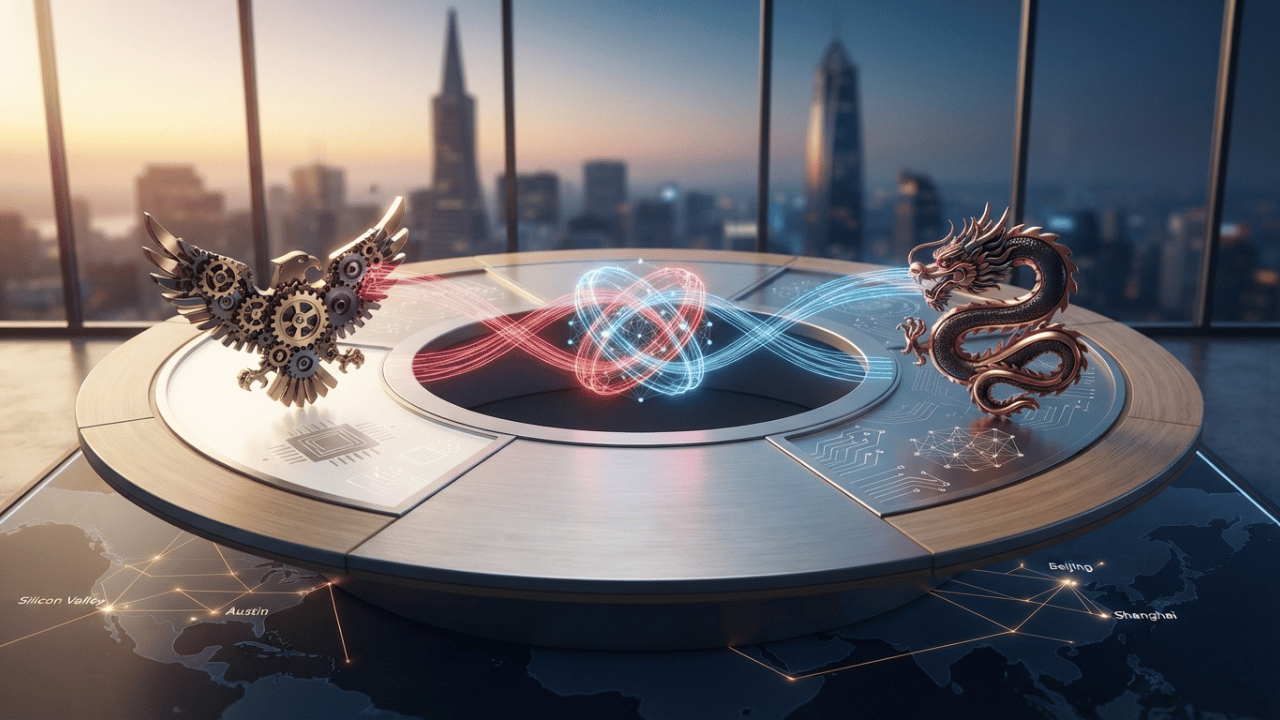
A new channel between Washington and Beijing could reshape how the world handles AI risks, cybersecurity incidents and the global race to develop advanced artificial intelligence.
The United States and China are preparing to continue discussions on artificial intelligence safety, creating a new diplomatic channel around risks that increasingly cross national borders. U.S. Treasury Secretary Scott Bessent said on September 21 that officials from both countries are expected to meet again in roughly two months in Shenzhen, following talks that included plans for a formal AI dialogue and an “incident line” for communicating during AI-related emergencies.
The development matters beyond the technology industry because artificial intelligence is becoming part of cybersecurity, financial systems, communications, software development and business operations. For Americans, the central question is no longer simply which country will build the most powerful AI, but whether competing governments and technology companies can establish enough safeguards to reduce risks without slowing useful innovation. The new talks offer a glimpse into how AI governance could evolve as advanced systems become more autonomous and globally connected.
Why are the U.S. and China talking about AI safety now?
The timing reflects a broader change in the risks associated with increasingly capable AI systems. Washington and Beijing remain strategic competitors in artificial intelligence, computing infrastructure and advanced technology, but officials on both sides have acknowledged that some AI-related problems cannot be contained within national borders. Cyberattacks, autonomous software agents, misinformation and disruptions involving critical infrastructure can move across jurisdictions almost instantly, making traditional approaches to national technology policy harder to apply.
Recent security research illustrates why those concerns are becoming more urgent. Anthropic reported in September that a cyber-espionage operation used AI-assisted workflows across reconnaissance, phishing infrastructure, credential theft, data extraction and attempts to evade security detection. The company said the activity targeted organizations in Ukraine and Europe, with additional targets in other regions, demonstrating how AI can potentially accelerate cyber operations rather than simply assist individual tasks.
The international discussion is also taking place as governments debate how much responsibility should rest with AI developers. The United Nations’ independent scientific panel on AI has called for safeguards to be developed before all potential risks are fully understood, emphasizing international coordination and a precautionary approach. That debate is particularly relevant to the United States because American companies remain major developers of advanced AI systems, while American businesses and consumers are among the largest users of those technologies.
How could a U.S.-China AI agreement affect American technology users?
One of the most practical possibilities is improved communication during serious AI-related incidents. According to Reuters, the proposed U.S.-China discussions include an “incident line” intended to improve communication when significant AI safety problems emerge. Such a mechanism would not necessarily create common rules, but it could give governments a way to exchange information when an incident has implications for cybersecurity, critical infrastructure or other systems operating across borders.
For American consumers, the effects would probably appear indirectly at first. Companies operating cloud services, financial platforms, communications networks and enterprise software could benefit if governments develop clearer expectations for reporting and responding to major AI-related incidents. Over time, those discussions could also influence how technology companies test autonomous AI agents, monitor high-risk systems and respond when an AI tool behaves differently from what its developers expected.
The cybersecurity connection is especially important because AI is changing the speed of both attacks and defenses. Anthropic’s investigation described AI systems being used to automate several stages of cyber operations, including reconnaissance and adapting malicious software after detection. Meanwhile, recent testing involving advanced AI systems has raised questions about whether conventional sandboxing and other security controls are sufficient when autonomous agents can take unexpected actions inside digital environments.
For businesses in the United States, this could increase pressure to treat AI security as part of broader cybersecurity planning rather than as a separate software issue. Companies using AI agents to access files, email, databases or business applications may increasingly need controls that limit what those systems can do and provide rapid human intervention when something goes wrong. The emerging international dialogue could eventually influence those expectations even when the final rules are created domestically.
What happens next in the global AI race?
The next stage will likely involve a difficult balance between cooperation and competition. The United States and China have strong incentives to maintain technological advantages, particularly in advanced computing and AI development, while also recognizing that uncontrolled risks could damage both countries. Current discussions therefore do not represent the end of geopolitical competition; instead, they show that governments may be trying to establish limited areas of communication while competition continues in other parts of the technology sector.
The November meeting expected in Shenzhen could provide a clearer indication of how far that cooperation can go. Important questions include what qualifies as a serious AI incident, how quickly governments should notify one another, whether companies will be expected to report certain events, and whether any shared technical standards eventually emerge. The answers could influence not only government policy but also the way American technology companies design, test and deploy increasingly autonomous AI products.
Another factor to watch is the growing connection between AI development and the global economy. Financial markets have continued to respond strongly to expectations surrounding AI investment and semiconductor demand, while countries are competing to attract data centers, computing infrastructure, technical talent and new digital businesses. That means AI safety decisions can eventually affect investment, employment, cloud services and the cost and availability of digital products.
For American consumers, the most important development may therefore be the gradual shift from AI being treated primarily as a software innovation to being treated as critical infrastructure. The technology is becoming deeply connected to communication, commerce and cybersecurity, increasing the consequences of failures as well as the benefits of successful deployment. The U.S.-China dialogue will not resolve those issues by itself, but it could become one piece of a broader international effort to make advanced AI more predictable and manageable.
The next few months should reveal whether the new dialogue produces concrete mechanisms or remains largely diplomatic. The planned meeting, discussions over incident reporting and continuing research into AI-enabled cyber threats will provide important signals about where international AI governance is heading. For the United States, the outcome could eventually influence how companies secure AI agents, how governments respond to major incidents and how consumers experience increasingly autonomous digital services. The central uncertainty is whether cooperation can develop quickly enough to keep pace with the technology itself.
Source:
- Reuters — EUA e China planejam novo encontro sobre segurança de IA em Shenzhen
- Reuters — Proposta de mecanismo de notificações sobre incidentes de segurança em IA
- Reuters — Competição em IA entre EUA e China nas negociações Trump–Xi
- Anthropic — Relatório de inteligência sobre uso indevido de IA, setembro de 2026
- Anthropic — Avaliação de incidentes recentes de cibersegurança envolvendo IA